

Why teams choose  ?
Make Gosu quality measurable across teams and releases.
Get clear risk visibility for leaders and actionable fixes for developers.
Why teams choose ?
Make Gosu quality measurable across teams and releases.
Get clear risk visibility for leaders and actionable fixes for developers.

Strategic visibility into code health
GoQu turns code quality into measurable indicators, allowing developers to discover security and performance issues, highlight Guidewire upgrade and migration requirements, prioritise critical areas and compare different systems and modules. This gives decision-makers a shared, objective view of the codebase, ownership and accountability for defects introduced to your project and a much stronger basis for prioritisation.
Technical debt expressed in money and effort
GoQu translates bugs, code smells and vulnerabilities into estimated effort and effective cost. With GoQu Quality Report, you will get a ranked list of what to fix first, with clear impact on budget and workload, code quality comparisons with other insurers in your market and actionable insights into your architecture. This makes it far easier to justify remediation spend and compare technical work with other business investments.
Reduced risk and fewer production incidents
By catching issues early and enforcing consistent standards, GoQu lowers the likelihood of failures in core policy, billing and claims systems. Fewer incidents mean fewer emergency releases, less unplanned overtime and fewer negative surprises for customers and operations. In practice, this protects both your brand and your margins.
Better planning and more predictable delivery
With time estimates and clear impact assessment, GoQu makes planning much more reliable. You can align stabilisation work, upgrades and new features on a realistic timeline, instead of constantly reacting to hidden defects. This improves predictability for both IT and business stakeholders and supports more confident roadmap commitments.
Compliance, security and a future-proof Guidewire platform
GoQu’s OWASP and CWE coverage helps you demonstrate that your systems follows recognised security and industry standards. Audit trails, severity ratings and structured reports make risk and compliance discussions easier and more evidence-based. Combined with regular updates aligned with Guidewire and SonarQube, it keeps your core platform safer today and easier to evolve tomorrow.
User-oriented development
We build GoQu together with its users. Over 50% of the features and improvements delivered in 2024 came directly from client requests. Your Gosu codebase is unique – and GoQu evolves to match your real development workflows, not the other way around.
Benefit from over 170 ready-to-use rules
GoQu currently provides 170+ pre-defined rules – and the list is still growing. You can modify and customise the behaviour of many rules to better fit your project and coding standards. Each rule is documented in depth, with code examples and references, so the whole team understands what is being checked and why.
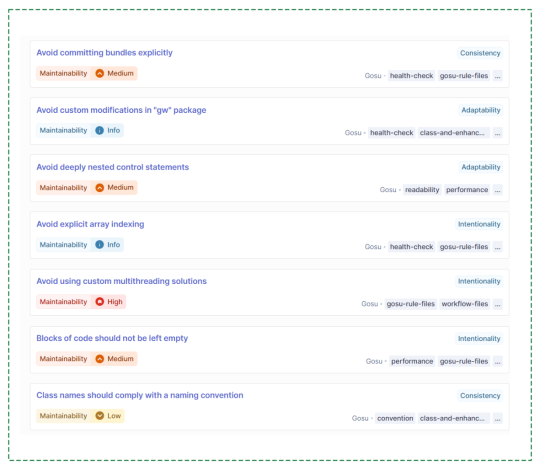
Time estimates for fixing issues
GoQu provides precise time frames for resolving issues detected in your code. This helps developers and team leads plan their work, estimate remediation effort and negotiate realistic timelines. Instead of guessing, you can base your planning on concrete numbers.
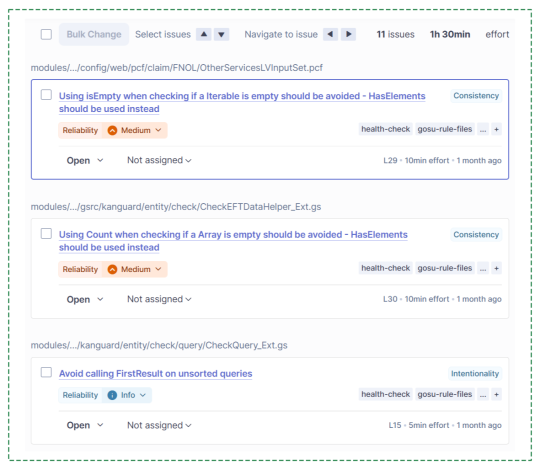
Compliance with OWASP & CWE standards
GoQu’s adherence to OWASP and CWE ensures that your applications are protected against common vulnerabilities. Issues are prioritised and rated according to global security standards, so your team can focus on resolving the most critical problems instead of debating priorities.
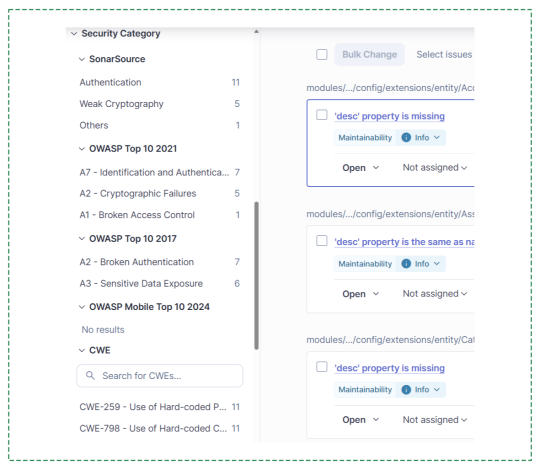
Seamless integration with Guidewire, SonarQube and Cloud
GoQu receives regular updates to remain compatible with the latest versions of Guidewire and SonarQube. It offers pull-request decorators, commit scope analysis, merge prevention and all out-of-the-box SonarQube features for the Gosu language. This lets you enhance your development workflow quickly, without changing your existing toolchain.
See the risks
before they slow you down
Schedule a GoQu Audit to identify critical issues, security vulnerabilities and structural risks in your Guidewire codebase — and get practical recommendations on what to fix first.

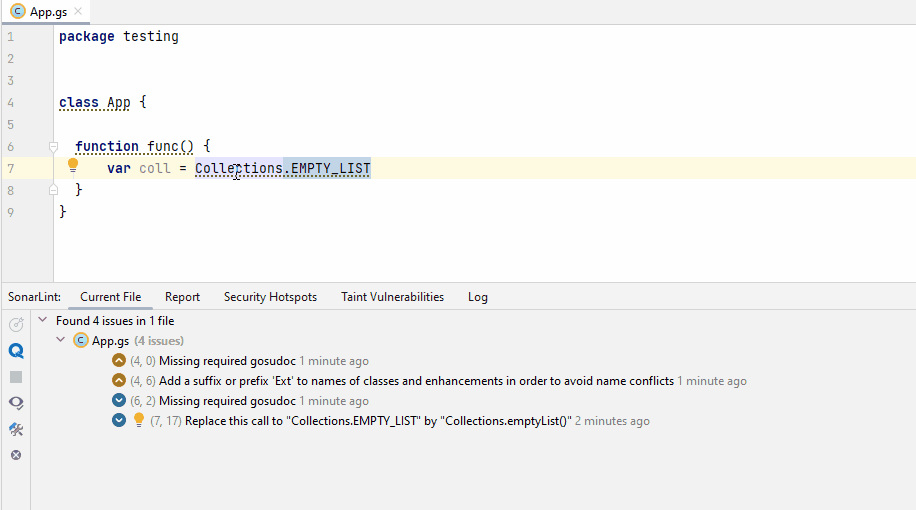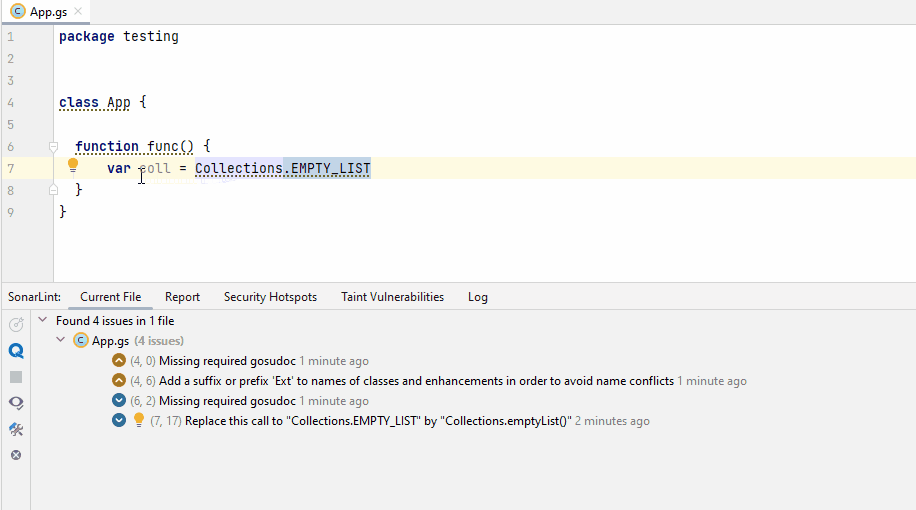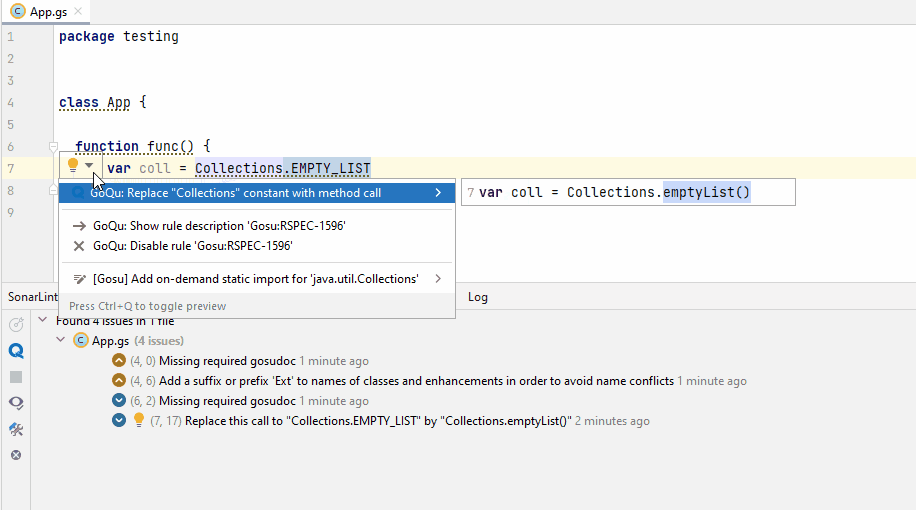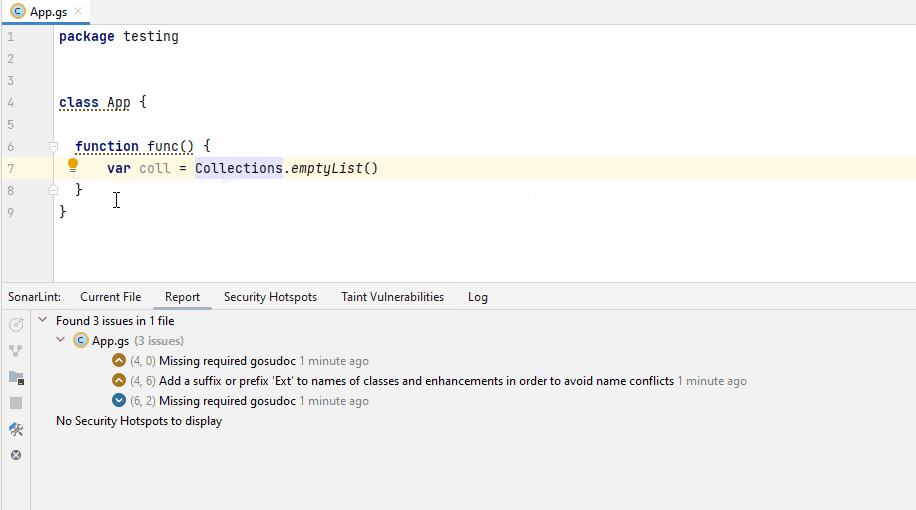
From IDE to pipeline: GoQu Dev, GoQu Hub & CARE in action
GoQu Dev helps developers spot and fix Gosu issues directly in their IDE, before they even reach the repository.
Contact
Łukasz Pietrucha
Head of Quality Assurance
Davide Santonocito
Sales Engineer